

A one-time pad is an encryption scheme that combines a plaintext with a uniformly random secret key of the same length, chosen independently of the plaintext and used only once. In its binary form, the ciphertext is obtained by bitwise XOR, and the same key recovers the plaintext,
 |  |  |
(1)
|
 |  |  |
(2)
|
Here  ,
 , and
 are binary strings
of length
 (Menezes et al. 1996, p. 192).
The scheme has perfect secrecy. For every plaintext  of positive probability
and every ciphertext
 ,
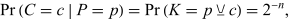 |
(3)
|
so the ciphertext is uniform and independent of the plaintext. In particular,
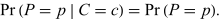 |
(4)
|
The plaintext need not itself be uniformly distributed.
If a key is reused for two plaintexts  and
 , then
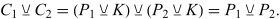 |
(5)
|
The two ciphertexts therefore reveal the bitwise XOR of the plaintexts, so key reuse does not provide perfect secrecy in general (Menezes et al. 1996, p. 21).
