

Homomorphic encryption is encryption that allows a computation on plaintext to be performed through a corresponding computation on ciphertext,
without first decrypting the data (Rivest et al. 1978, pp. 172-173; Numberphile
2016). For an allowed binary operation  on plaintext, a corresponding
operation
 on ciphertext must be
computable without the decryption key and return valid ciphertext.
It must satisfy
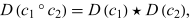 |
where  denotes decryption and
 and
 are valid ciphertexts for
which the operation is supported. This homomorphism
condition does not by itself establish cryptographic security.
For example, for valid keys the unpadded RSA cryptosystem encrypts integer representatives  and
 , with
 and
 , using
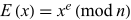 . The identity
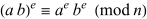 |
shows that multiplication of ciphertexts modulo  encrypts the product of their plaintexts
modulo
 (Rivest et al. 1978, pp. 175-176). This preserves multiplication,
but does not in general preserve addition.
